Short Answer
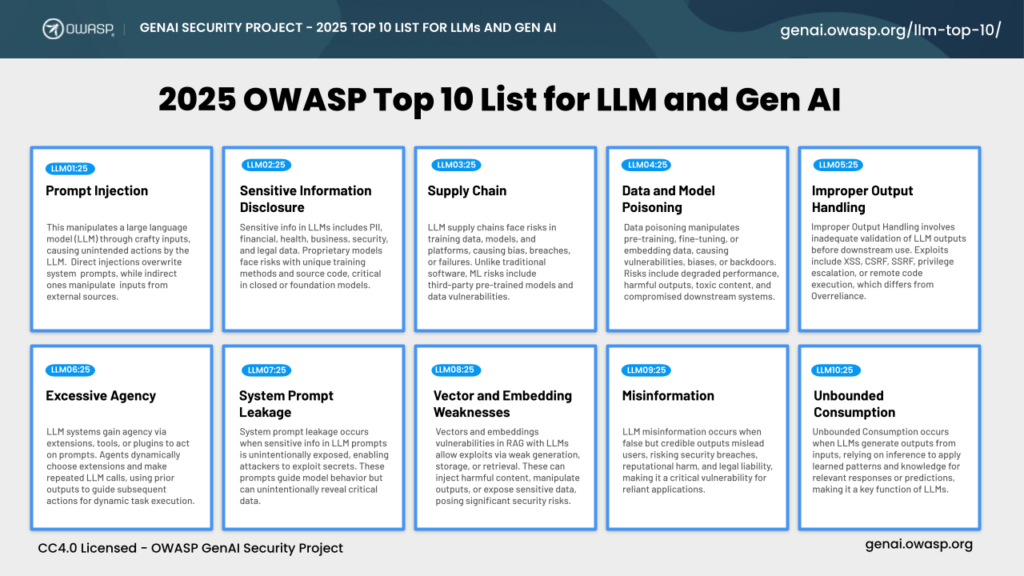
The Open Web Application Security Project (OWASP) has long been the harbinger of web security standards, and its Top 10 list serves as a barometer for assessing the prevailing risks faced by organizations globally. As we now turn our eyes to the latest iteration, the OWASP Top 10 Risks of 2025, we witness how the security landscape has morphed, influenced by technological advancements, changing development methodologies, and evolving threat vectors. This article delves into the updated list, examining what has shifted and what it reveals about the current state of web security.
1. Insecure Design
The first item on the 2025 list is a significant departure from previous iterations. While ‘Insecure Design’ was hinted at before, it has now emerged as a standalone risk. Organizations increasingly rely on complex architecture, and the failure to embed security into the design stage has led to vulnerabilities that can be devastating when exploited. The rise of agile methodologies often neglects security during the early phases of development. This gap emphasizes the need for a shift in mindset: security must be a foundational aspect rather than an afterthought.
2. Authentication and Session Management Failures
Persistent vulnerabilities in authentication mechanisms remain a critical issue. The OWASP Top 10 list emphasizes that, despite advances, many organizations still struggle with implementing robust session management practices. Misconfigured session timeouts, inadequate password policies, and session fixation vulnerabilities often plague systems. As cybercriminals become increasingly sophisticated, the necessity for multifactor authentication and comprehensive session management cannot be overstated. This evolution represents an invitation for organizations to reexamine their user authentication strategies continually.
3. Injection Flaws
Injection attacks have endured as a perennial threat. While perhaps expected, their continued prevalence reflects inadequate remediation efforts by developers. SQL injection, XML injection, and command injection remain potent weapons in the hands of attackers. This updated risk recognizes the synergy between the rise of API-centric applications and the complex interactions they entail. The spotlight on injections serves as a reminder: every piece of data should be treated as suspicious, necessitating stringent validation protocols throughout application lifecycles.
4. Security Misconfigurations
Security misconfigurations remain a cornerstone on the Top 10 list, albeit with a nuanced understanding that encompasses the complexity of modern infrastructures. Cloud configurations, containerization, and third-party integrations are often neglected, leading to unintentional exposure of sensitive data and services. The emergence of DevSecOps highlights the need for continuous security assessments and proactive vulnerability management, underscoring the intricate dependencies within today’s applications.
5. Vulnerable and Outdated Components
The inclusion of this risk serves as a stark reminder of the inherent dangers associated with reliance on third-party libraries and frameworks. As the pace of development accelerates, so too does the propensity for organizations to incorporate these components without adequate scrutiny. Attacks exploiting known vulnerabilities in outdated libraries pose significant risks. The onus is on developers to maintain a diligent stance concerning component management — thereby necessitating regular updates and patches to mitigate potential threats.
6. Insufficient Logging and Monitoring
The risk pertaining to insufficient logging and monitoring has gained traction as cyberattacks become more sophisticated and stealthy. Without the capability to log and monitor real-time activities effectively, organizations are often ill-prepared to detect intrusions or respond to incidents promptly. This oversight can prolong the impact of breaches. Implementing comprehensive logging, paired with continuous monitoring and analysis, allows organizations to cultivate a posture of readiness against impending threats.
7. Server-Side Request Forgery (SSRF)
The emergence of Server-Side Request Forgery (SSRF) in the latest Top 10 highlights an increasing trend of leveraging server-side functionality for nefarious purposes. Attackers can manipulate server requests to retrieve sensitive internal data or trigger unintended actions. This risk amplifies the importance of validating user inputs and restricting server-side capabilities. As reliance on cloud services and microservices grows, awareness and prevention of SSRF vulnerabilities have become indispensable.
8. Cross-Site Scripting (XSS)
Cross-Site Scripting vulnerabilities have reclaimed their place as a critical risk, illustrating the ongoing challenge developers face in safeguarding user interactions. Despite the availability of well-established mitigation strategies, XSS remains prevalent due to lapses in input validation and output encoding practices. Given the intricate nature of modern web applications, fostering a deeper understanding of user-generated content handling is paramount to provide robust defenses against XSS exploits.
9. Insufficient Access Controls
The pervasive issue of insufficient access controls has been redefined in the context of distributed environments. With the expansion of remote work and cloud-based applications, unauthorized access to sensitive resources can have dire consequences. Organizations must implement granular access control mechanisms and adhere to the principle of least privilege to ensure that users are limited to only what they require. This enforcement is essential to reducing the attack surface and containing potential breaches.
10. Business Logic Vulnerabilities
Finally, the inclusion of business logic vulnerabilities signals a recognition of the nuanced ways attackers exploit system design flaws. These vulnerabilities arise from flawed business processes or workflows, allowing malicious actors to manipulate applications to achieve unauthorized outcomes. Organizations must prioritize business logic security assessments, integrating them into the design process to fortify their systems against these particular threats. The complexity involved in evaluating business logic requires collaboration across development and security teams.
In summation, the OWASP Top 10 Risks of 2025 extends beyond mere enumeration; it reflects a landscape evolving in tandem with technology, methodologies, and the relentless ingenuity of cyber adversaries. Understanding these emerging risks is essential for organizations striving to bolster their security postures. As we gaze ahead, it becomes increasingly clear that a proactive approach, integrating robust security measures at every stage of development, is not merely advisable—it is imperative for safeguarding the integrity, privacy, and trust that underpin today’s digital ecosystem.
FAQ
What is the OWASP Top 10 list?
The OWASP Top 10 is a regularly updated list of the most critical security risks to web applications, published by the Open Web Application Security Project to guide developers and organizations in improving security.
What are the major changes in the OWASP Top 10 Risks for 2025?
Key changes include the addition of Insecure Design as a standalone risk, the emergence of Server-Side Request Forgery (SSRF), and a renewed focus on business logic vulnerabilities, reflecting evolving security challenges.
Why is 'Insecure Design' a critical risk in 2025?
‘Insecure Design’ highlights vulnerabilities introduced by failing to embed security into application design phases, especially with agile methodologies that may overlook early security considerations.
How can organizations mitigate these OWASP Top 10 risks?
Organizations should integrate security from the earliest design stages, implement strong authentication and session management, update and monitor components regularly, and adopt continuous security assessments such as DevSecOps.
FAQ
What is the OWASP Top 10?
The OWASP Top 10 is a list of the most critical web application security risks identified by the Open Web Application Security Project, updated periodically to reflect emerging threats.
Why is 'Insecure Design' a new risk in the 2025 list?
‘Insecure Design’ has emerged as a standalone risk due to the increasing complexity of architectures and the neglect of integrating security early in the design phase, especially with agile development practices.
How can organizations mitigate Authentication and Session Management Failures?
Implementing multifactor authentication, enforcing strong password policies, and ensuring proper session timeout and management practices can help mitigate these failures.
What is Server-Side Request Forgery (SSRF)?
SSRF is a vulnerability where attackers manipulate server-side requests to access or perform unauthorized actions on internal systems, often exploiting cloud and microservice infrastructures.
Why is continuous logging and monitoring important in web security?
Continuous logging and monitoring enable organizations to detect intrusions promptly and respond effectively, minimizing the impact of cyberattacks.
FAQ
What is the OWASP Top 10?
The OWASP Top 10 is a list of the most critical web application security risks, published by the Open Web Application Security Project, intended to raise awareness and guide organizations in mitigating common vulnerabilities.
What new risks are introduced in the OWASP Top 10 for 2025?
The 2025 list introduces risks such as Insecure Design, Server-Side Request Forgery (SSRF), and Business Logic Vulnerabilities, reflecting evolving threats in web application security.
Why is Insecure Design important in web security?
Insecure Design emphasizes embedding security into the architecture and design phases of development, preventing vulnerabilities before they arise rather than addressing them later.
How can organizations address insufficient logging and monitoring?
Organizations should implement comprehensive real-time logging and continuous monitoring systems to detect and respond promptly to security incidents.
What role does DevSecOps play in mitigating OWASP Top 10 risks?
DevSecOps integrates security practices into the development lifecycle, ensuring continuous security assessments and proactive vulnerability management.
Leave a Reply